Third-Party & Supply Chain Risk
Software Supply Chain Attacks Are Hiding in Your Dependencies
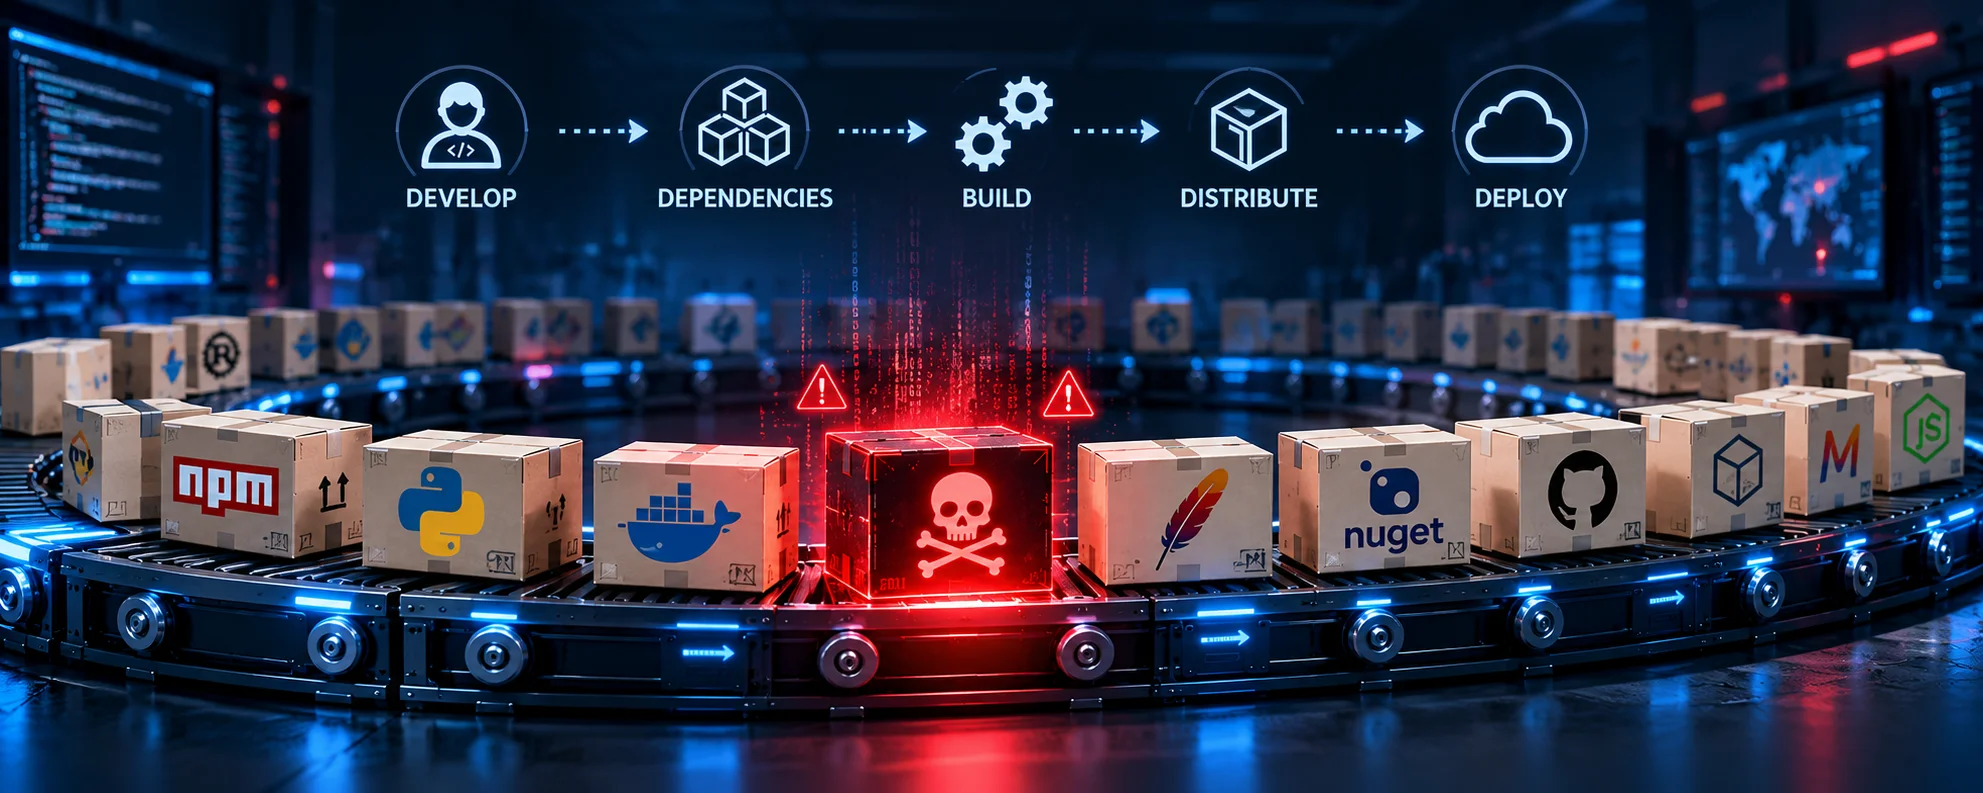
Software supply chain attacks exploit vulnerabilities in third-party dependencies, compromised packages, and CI/CD pipelines. Learn how these threats affect modern applications and the security measures organizations can implement to protect software integrity.