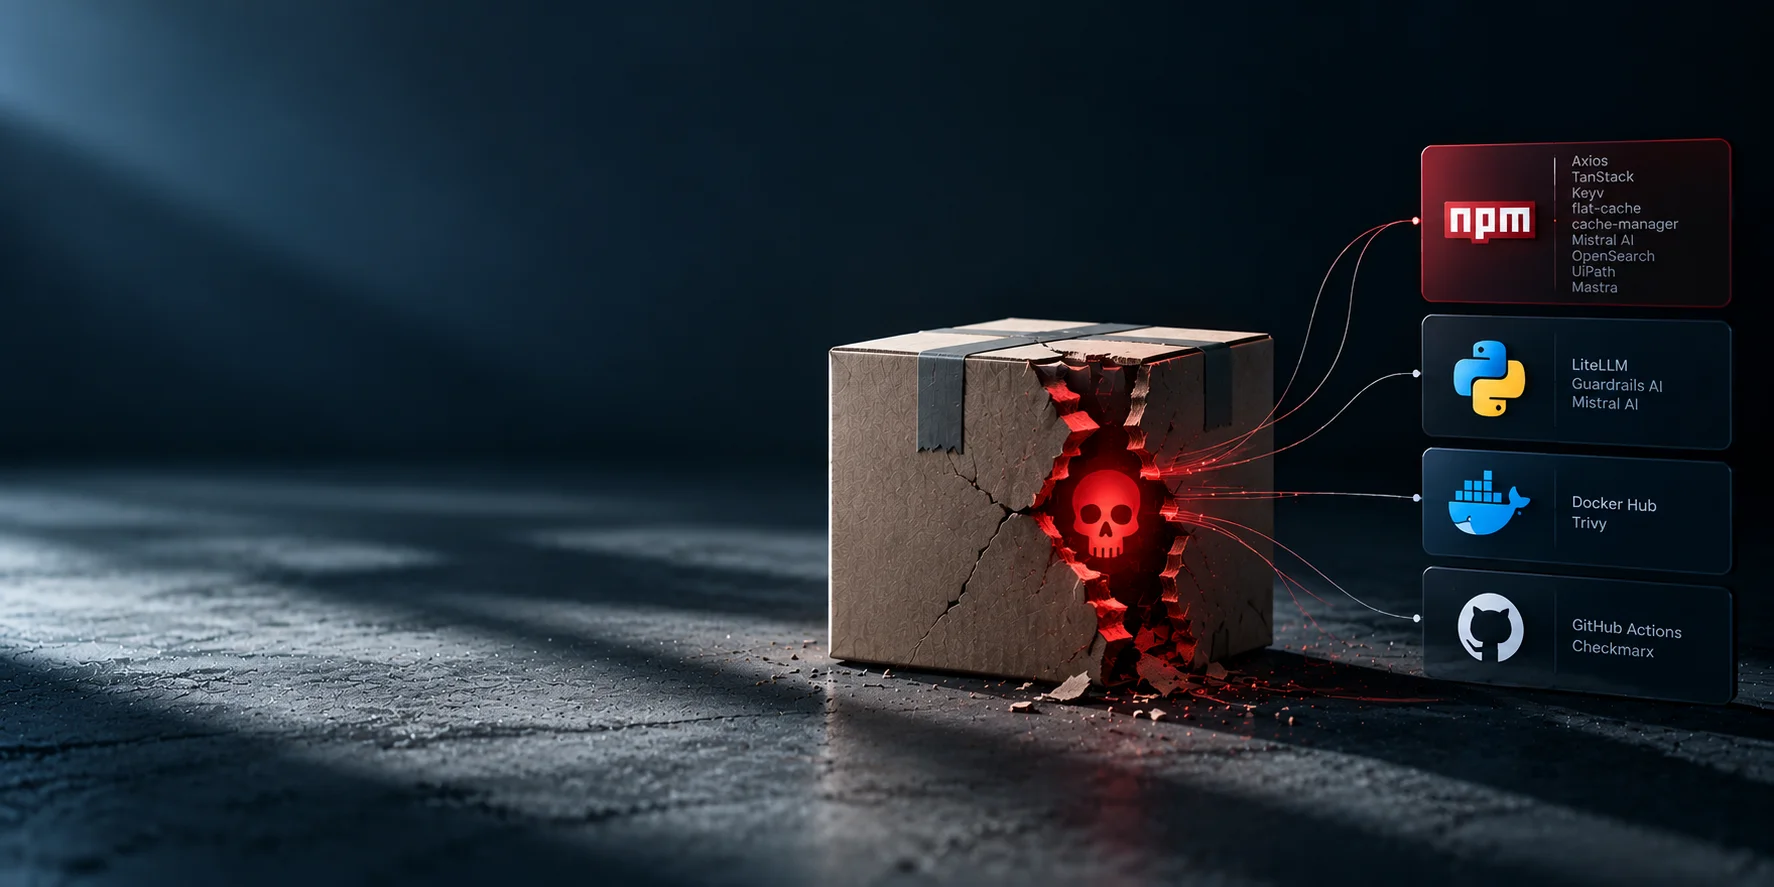
Third-Party & Supply Chain Risk
When Trusted Software Becomes the Attack Vector
organizations rely on trusted software vendors, signed updates, and established distribution channels to maintain their systems. However, trust in a software provider does not guarantee that every update or component is secure. If attackers compromise a vendor's development environment or distribution infrastructure, legitimate software can become a delivery mechanism for malicious code.