Why Vendor Security Assessments Fail to Prevent Supply Chain Risk
Vendor questionnaires and certifications provide only a partial view of security
A vendor can pass a security questionnaire, provide industry-recognized certifications, and demonstrate documented security policies while still introducing significant risk into an organization's environment. The problem is not that assessments have no value. It is that third-party vendor security risk cannot be measured accurately through documentation alone.
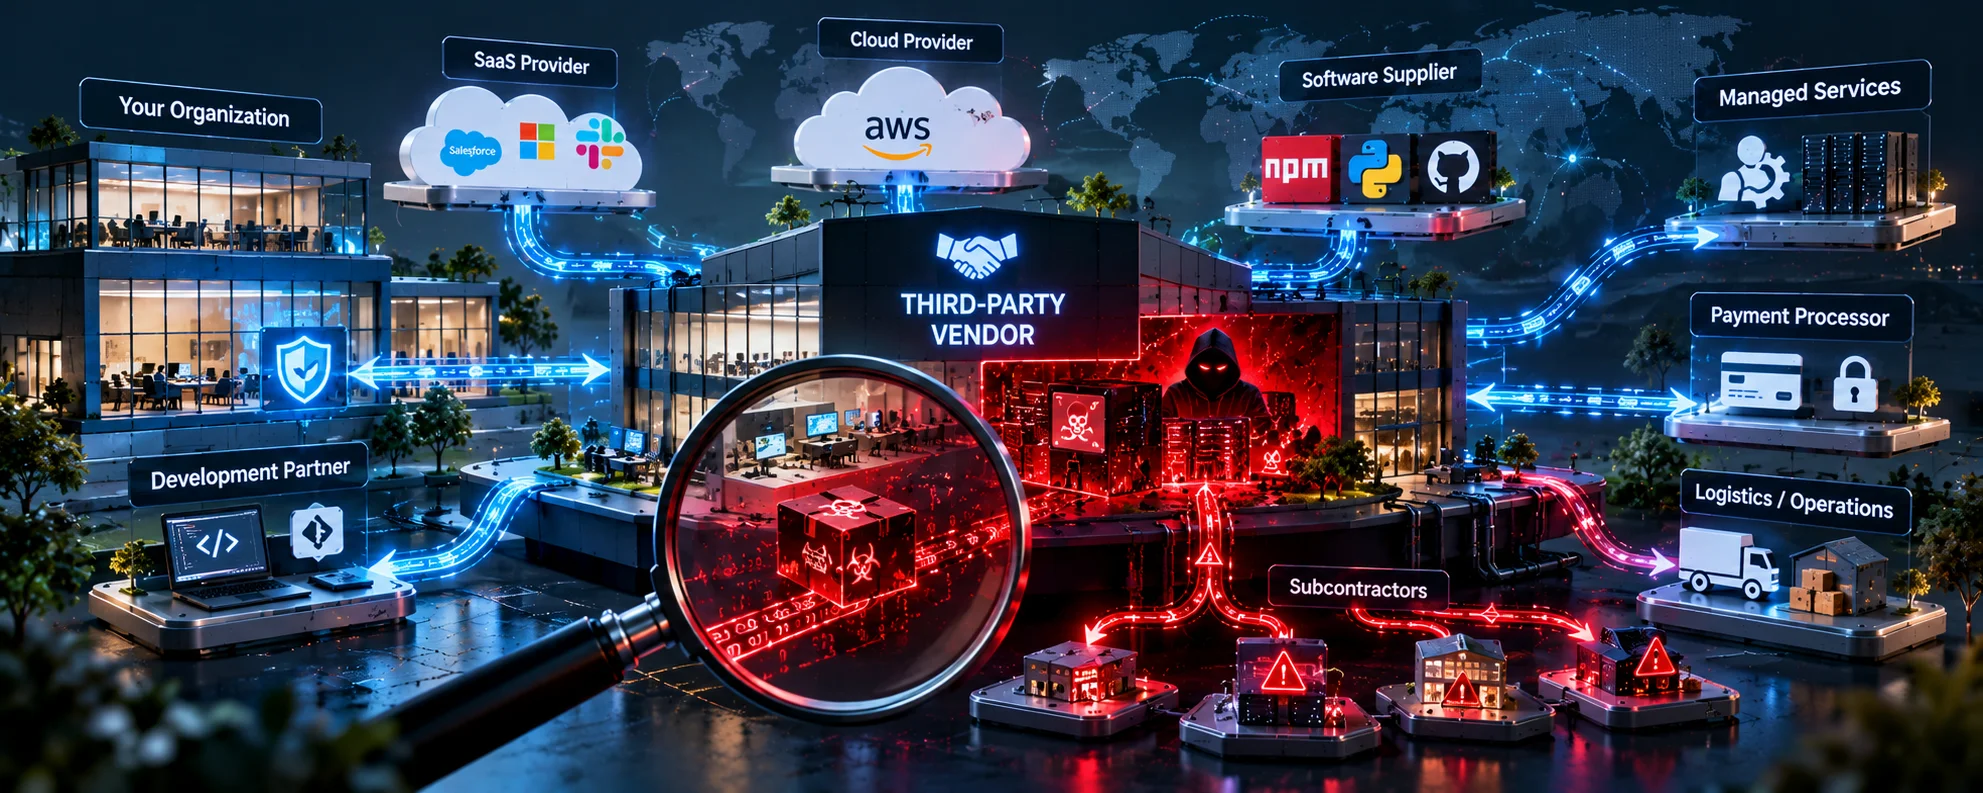
Organizations depend on external providers for software, cloud infrastructure, payment processing, identity management, development services, and business operations. These relationships can give vendors access to sensitive information, production systems, privileged credentials, and critical business processes. A weakness in one provider can therefore affect multiple customers.
Traditional vendor assessments often establish whether a supplier has documented security controls. They may not establish whether those controls work effectively, whether the supplier's environment has changed, or whether its access creates an unacceptable level of exposure.
Reducing supply chain risk requires a more complete approach: assess the vendor, understand the integration, validate critical controls, and monitor the relationship throughout its lifecycle.
Why Traditional Vendor Security Assessments Fall Short
Vendor security assessments commonly rely on questionnaires, policy documents, audit reports, and compliance certifications. These provide useful evidence, but each has limitations.
1. Questionnaires measure reported controls, not necessarily their effectiveness
A vendor may confirm that it uses multifactor authentication, encrypts sensitive information, performs vulnerability assessments, and maintains an incident response plan. Those answers do not independently verify implementation.
For example, a vendor may enforce multifactor authentication for employee accounts while allowing service accounts or legacy integrations to authenticate using long-lived credentials. A questionnaire might not reveal that distinction unless the questions are sufficiently specific and supported by technical evidence.
2. Certifications have a defined scope
A certification or independent audit report provides assurance about the controls, systems, locations, and period covered by the assessment. It does not automatically establish that every product, subsidiary, hosting environment, or integration operated by the vendor has equivalent protection.
Organizations should examine the report's scope, exclusions, assessment period, and any exceptions before treating it as evidence of security across the entire relationship.
3. Assessments become outdated
A vendor's risk profile can change after the initial review. It may introduce a new subprocessor, migrate infrastructure, change authentication mechanisms, experience a security incident, or acquire another company.
An assessment completed months earlier cannot reliably reflect every subsequent change. Without periodic reassessment and event-driven reviews, organizations may continue relying on assumptions that are no longer valid.
The Risk Often Exists in the Integration
The most significant exposure may not be the vendor's own infrastructure. It may be the connection between the vendor and the customer.
Consider a service provider that integrates with an organization's cloud environment. To perform its work, the provider receives API credentials with permission to access production resources. Even if the provider has documented security policies, compromised credentials could allow an attacker to misuse the granted permissions.
The same problem can occur with:
1. Third-party applications connected to corporate identity providers.
2. CI/CD integrations that can read source code or publish build artifacts.
3. Support providers with remote access to production systems.
4. SaaS platforms that process confidential business or customer information.
5. Vendors with access to cloud storage, databases, email systems, or security tooling.
These integrations create trust relationships that must be assessed independently of the vendor's general security posture.
A useful assessment should establish what data the vendor can access, which systems it can reach, what actions it can perform, and whether its access is restricted to the minimum required. It should also examine how credentials are issued, stored, rotated, monitored, and revoked.
Common Gaps in Third-Party Risk Management
Several recurring gaps can undermine an otherwise mature vendor risk program.
Incomplete vendor inventory: Organizations may not know every external service processing their data or accessing their systems. Business teams can adopt SaaS tools, developers can introduce third-party services, and suppliers can engage subcontractors without the security team receiving timely notification.
Insufficient risk classification: Applying the same assessment to every supplier wastes resources and can leave critical relationships underexamined. A vendor with access to production infrastructure presents a different level of risk from a supplier that provides a non-sensitive service without system access.
Limited technical validation: A vendor's statements should be supported by evidence proportionate to the risk. Depending on the service, this might include independent test summaries, configuration evidence, vulnerability management records, access-control demonstrations, or architecture reviews.
Weak subcontractor visibility: A supplier may depend on additional cloud providers, software vendors, support partners, or development teams. These downstream relationships can introduce further exposure. Organizations should understand material dependencies and determine how security requirements are communicated throughout the supply chain.
No effective exit process: Vendor offboarding is a security control, not just a procurement task. If a contract ends but API keys, user accounts, certificates, OAuth grants, or remote-access paths remain active, the former provider may retain unintended access.
How to Improve Third-Party Vendor Security Risk Management
A stronger program combines documented assurance with technical evidence and ongoing oversight.
1. Maintain a Complete Vendor Inventory
Record vendors, the services they provide, business owners, data classifications, system integrations, access privileges, and relevant subcontractors. Include both direct suppliers and material dependencies where they affect the organization's security.
This inventory establishes the foundation for prioritizing assessments and identifying relationships that require additional scrutiny.
2. Apply Risk-Based Assessment
Classify vendors according to the sensitivity of the data they process, their level of system access, their business criticality, and the consequences of a compromise.
High-risk vendors may require deeper technical reviews, independent assessment reports, security testing evidence, and formal remediation commitments. Lower-risk vendors may need a proportionate review rather than the same extensive process.
3. Validate Critical Security Controls
Do not rely exclusively on yes-or-no answers. Verify important controls using evidence appropriate to the relationship.
Examples include checking whether privileged access requires multifactor authentication, reviewing the vendor's incident notification commitments, examining vulnerability remediation practices, and confirming that sensitive data is protected in transit and at rest.
For software suppliers, review secure development practices, software update integrity, dependency management, and relevant software provenance information.
4. Restrict and Monitor Vendor Access
Use least privilege, scoped credentials, time-limited access where practical, and controlled administrative sessions. Monitor vendor activity for unusual authentication patterns, unexpected data access, privilege changes, and activity outside approved support windows.
Vendor access should be reviewed periodically and revoked promptly when it is no longer required.
5. Establish Continuous Monitoring and Reassessment
Reassess vendors when meaningful changes occur, not only when a calendar reminder arrives. Relevant triggers include major service changes, security incidents, changes in subprocessors, new system integrations, and changes in the data being shared.
Define who owns the relationship, how risks are escalated, what evidence must be refreshed, and which findings require remediation before the service can continue.
6. Define Contractual Security Requirements
Contracts should specify applicable security obligations, access restrictions, incident notification expectations, cooperation during investigations, data handling requirements, subcontractor obligations, and secure termination procedures.
The organization should also define how unresolved findings are handled. A critical issue may require remediation before onboarding, while a lower-risk finding may be managed through a documented exception with an owner and deadline.
These practices align with the risk-based approach described in the NIST Cybersecurity Supply Chain Risk Management guidance. NIST's due diligence guidance also emphasizes evaluating supplier provenance, resilience, foundational cyber practices, and supply chain relationships rather than treating supplier assurance as a questionnaire exercise alone.
Vendor Assurance Must Continue After Approval
Vendor approval should not be treated as a permanent security status. It is a decision based on the evidence and business context available at a particular time.
Organizations need a repeatable process for reviewing vendor changes, tracking remediation commitments, validating critical controls, and removing unnecessary access. Procurement, legal, engineering, IT, and security teams should share responsibility for maintaining an accurate view of vendor risk.
The objective is not to eliminate third-party relationships. It is to understand the exposure those relationships create and ensure that the risk remains within acceptable limits.
Conclusion
Third-party vendor security risk cannot be managed effectively through questionnaires and certifications alone. These tools provide useful assurance, but they do not replace technical validation, integration reviews, access monitoring, and continuous reassessment.
Organizations should prioritize vendors based on their access and business impact, verify the controls that matter most, and establish clear accountability throughout each supplier relationship.
Even a well-assessed vendor can experience a compromise. Organizations therefore need to understand not only how to evaluate suppliers, but also how to respond when trusted software or a service provider becomes part of an attack.
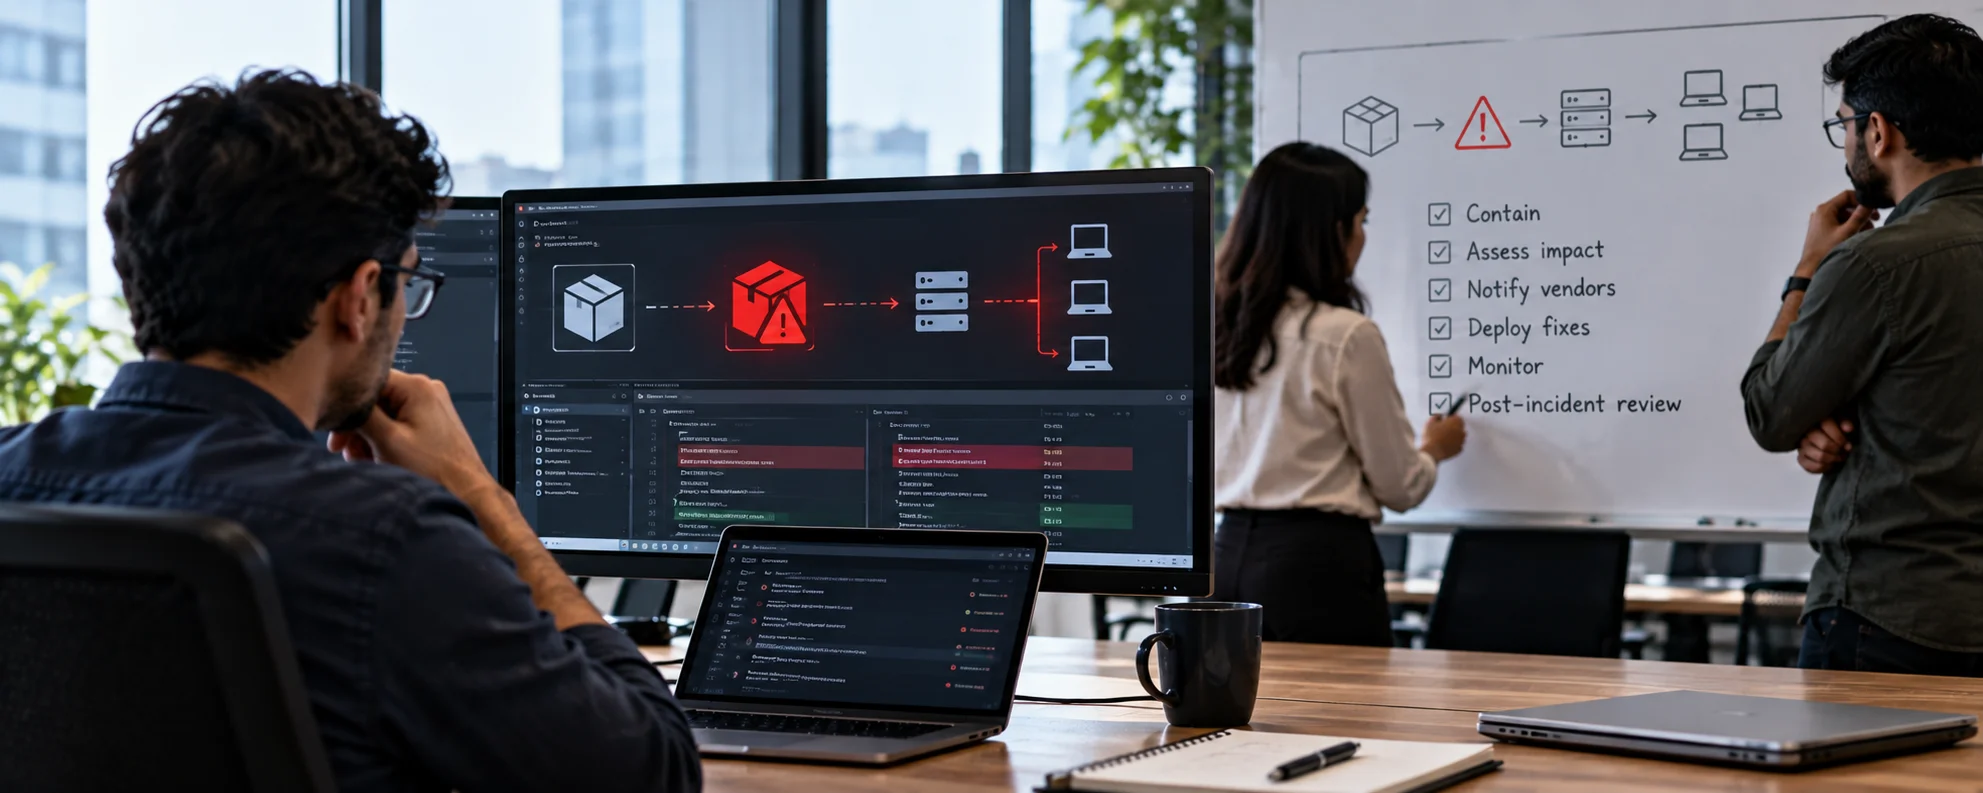
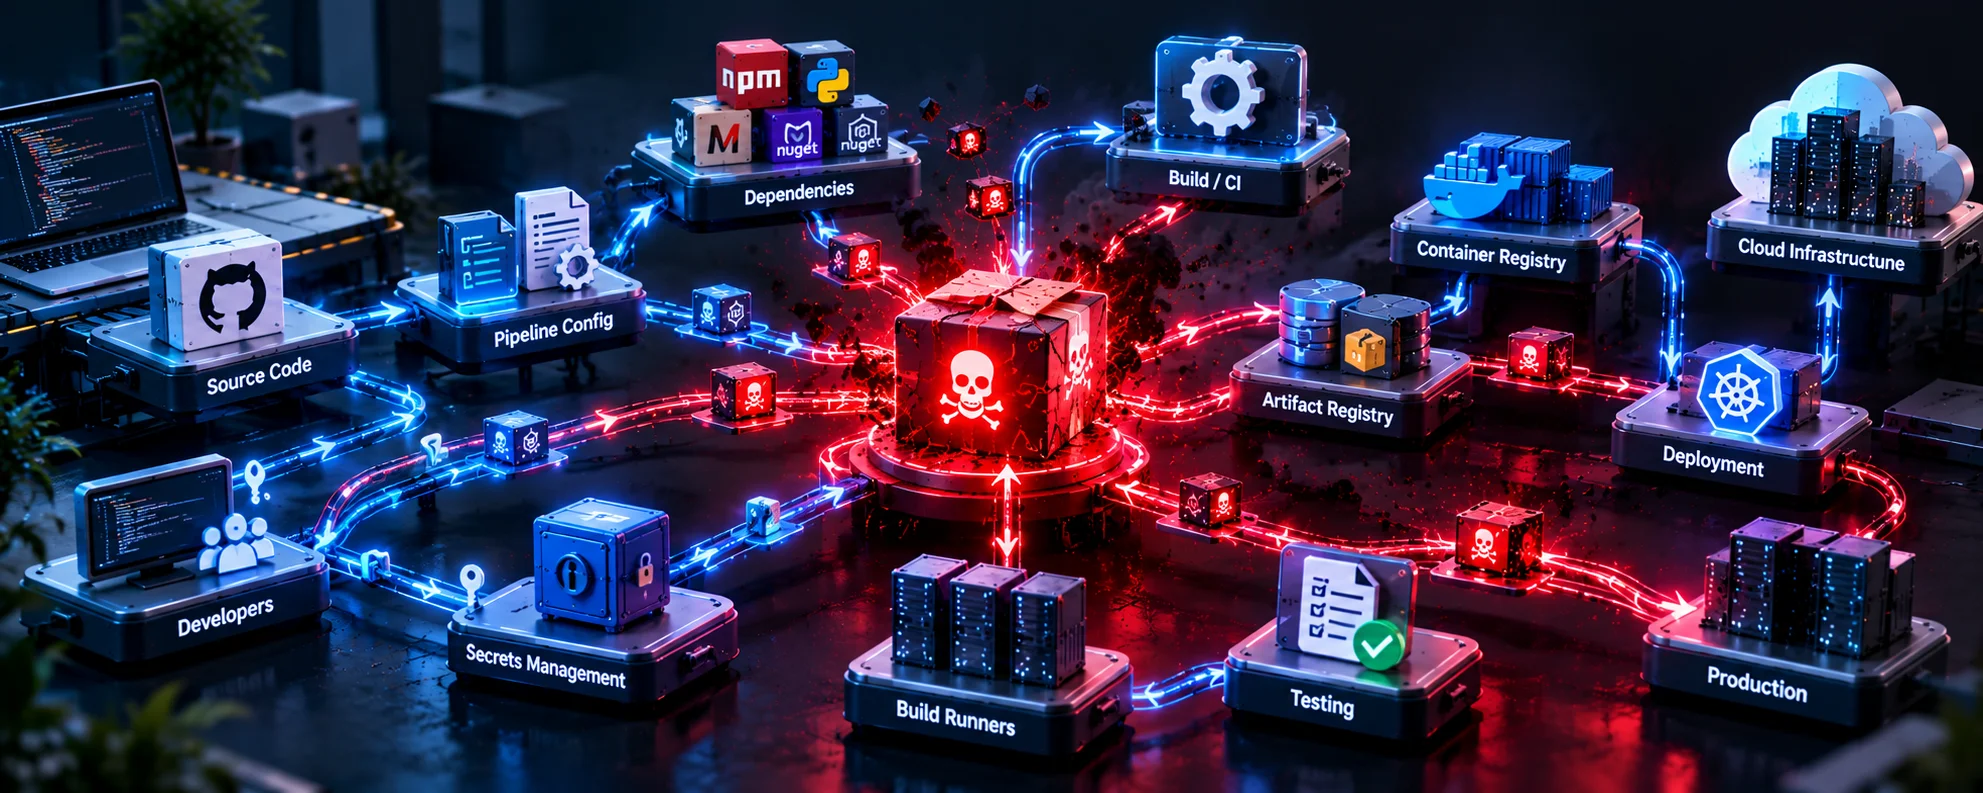
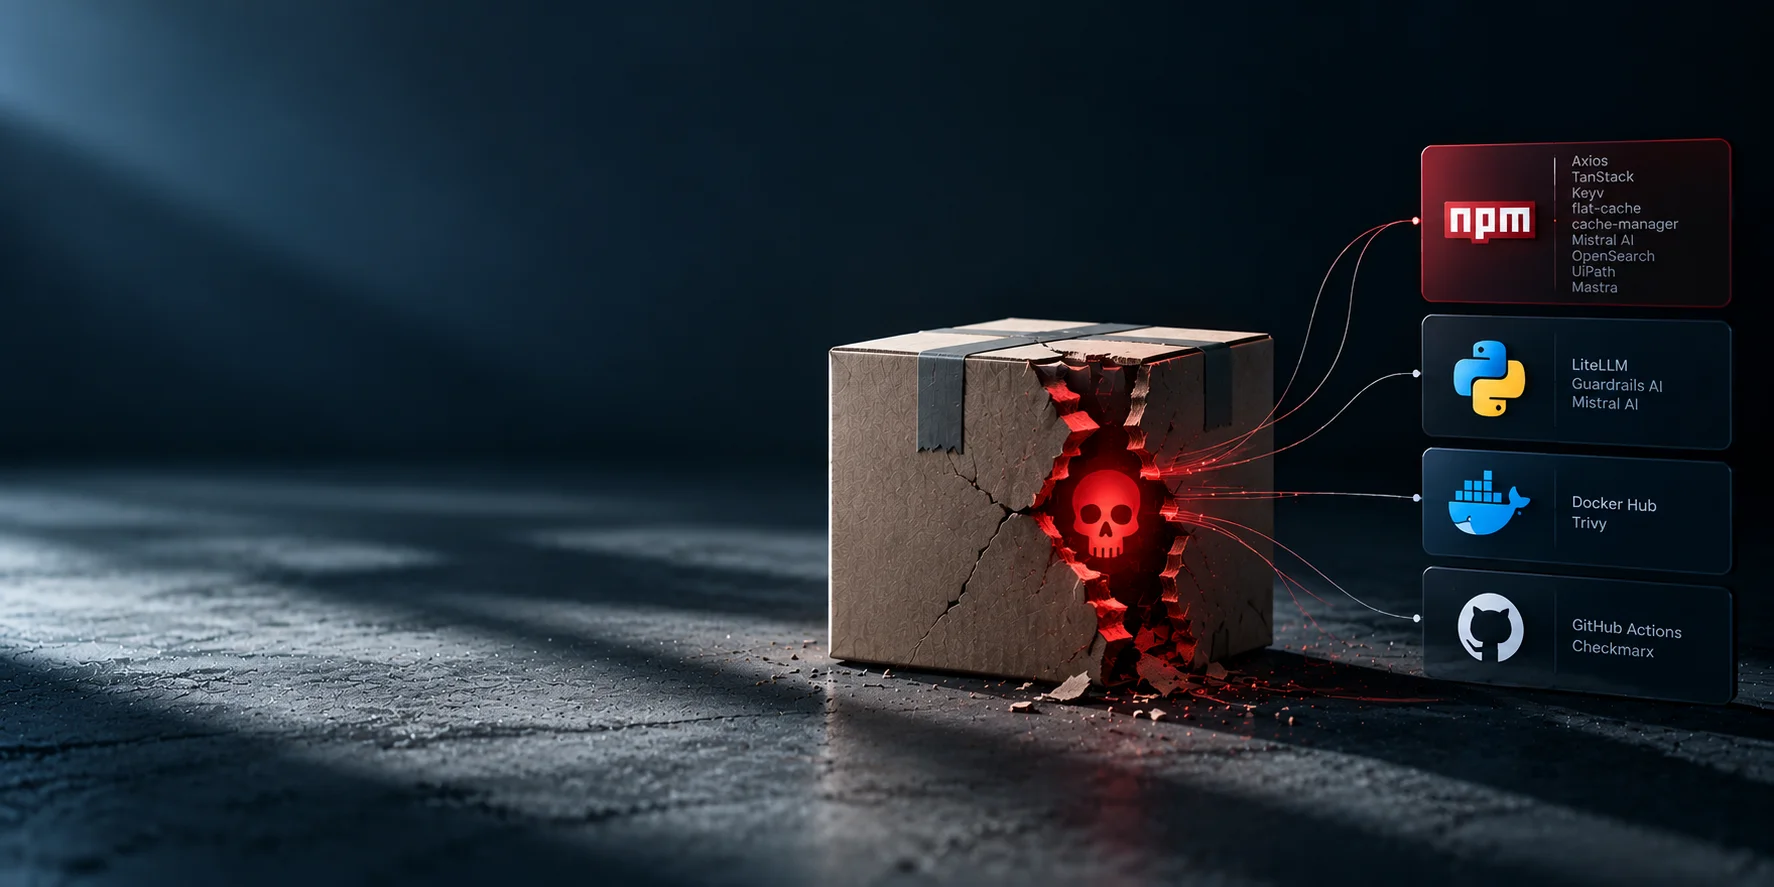
For a related perspective, read our article on how trusted software can become an attack vector. Once a compromise occurs, a defined software supply chain incident response process helps teams identify exposure, contain the incident, and restore trust.
Comments
No comments yet — start the conversation.