HomeAboutServices Pricing Platform Nprint ESPM DomTail Threat Map FlowGround Explore All Products → Disciplines CapabilitiesBlogContact

Insights From The Front Line

Research, field notes and practical guidance from the people who break into systems for a living, so you can defend yours.

Tagged #software supply chain security

Clear filters
Third-Party & Supply Chain Risk

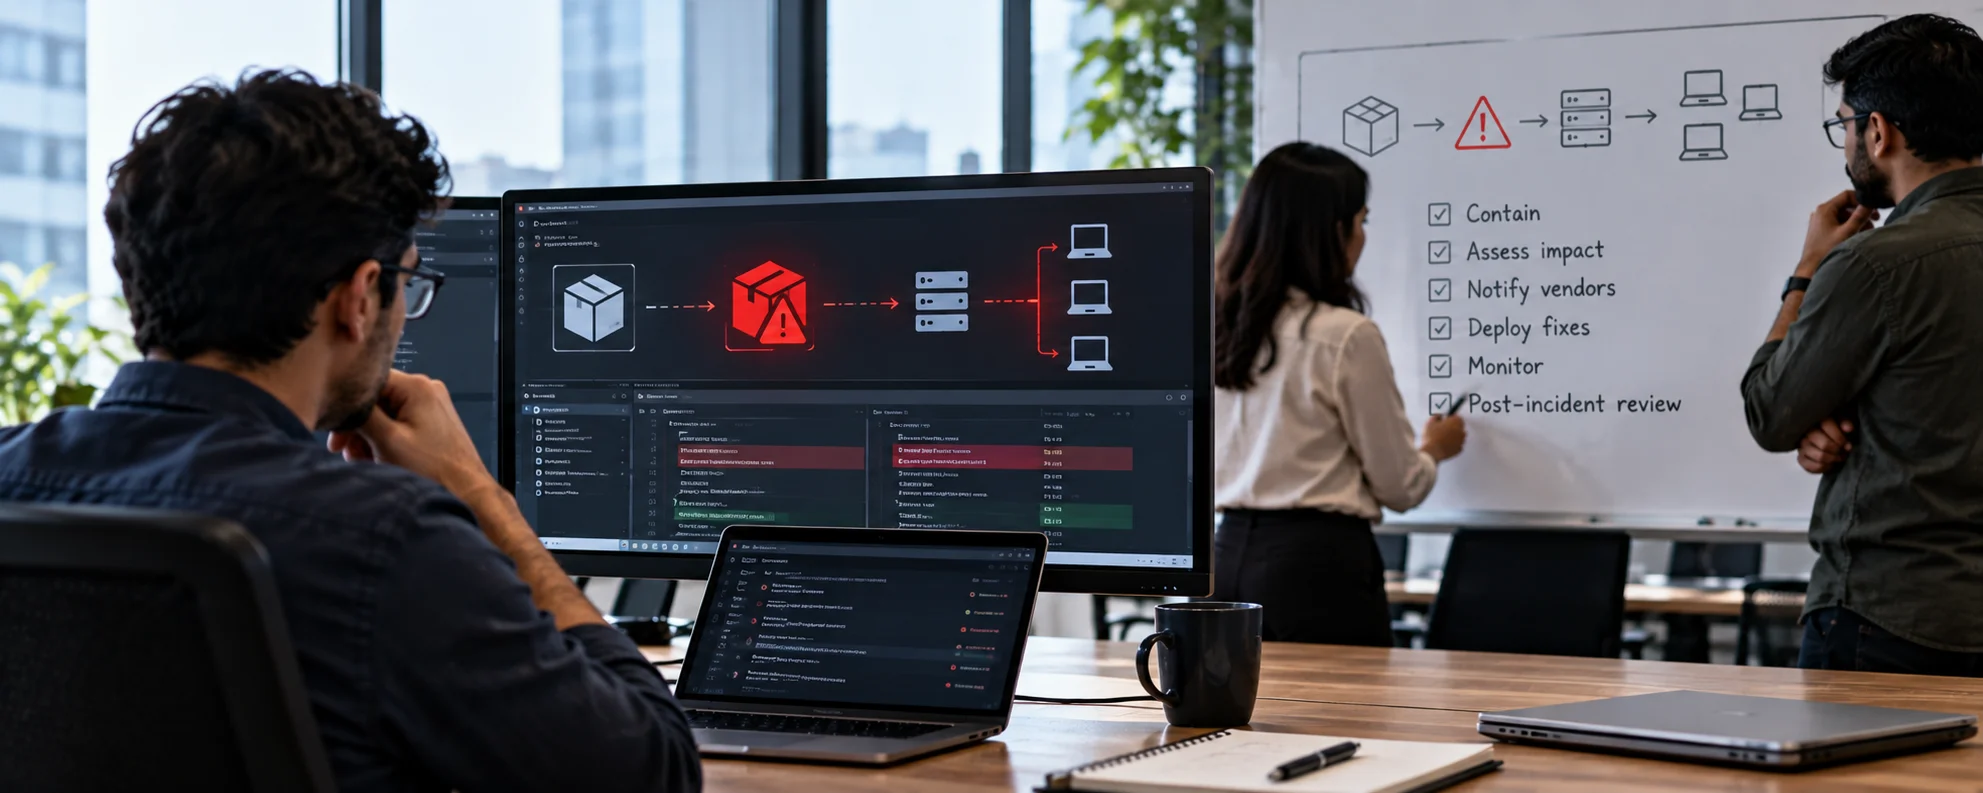
Responding to a Software Supply Chain Compromise

A software supply chain compromise can affect multiple applications, development environments, and production systems simultaneously. Identifying the affected component is only the first step.…
· 4 min read
Third-Party & Supply Chain Risk

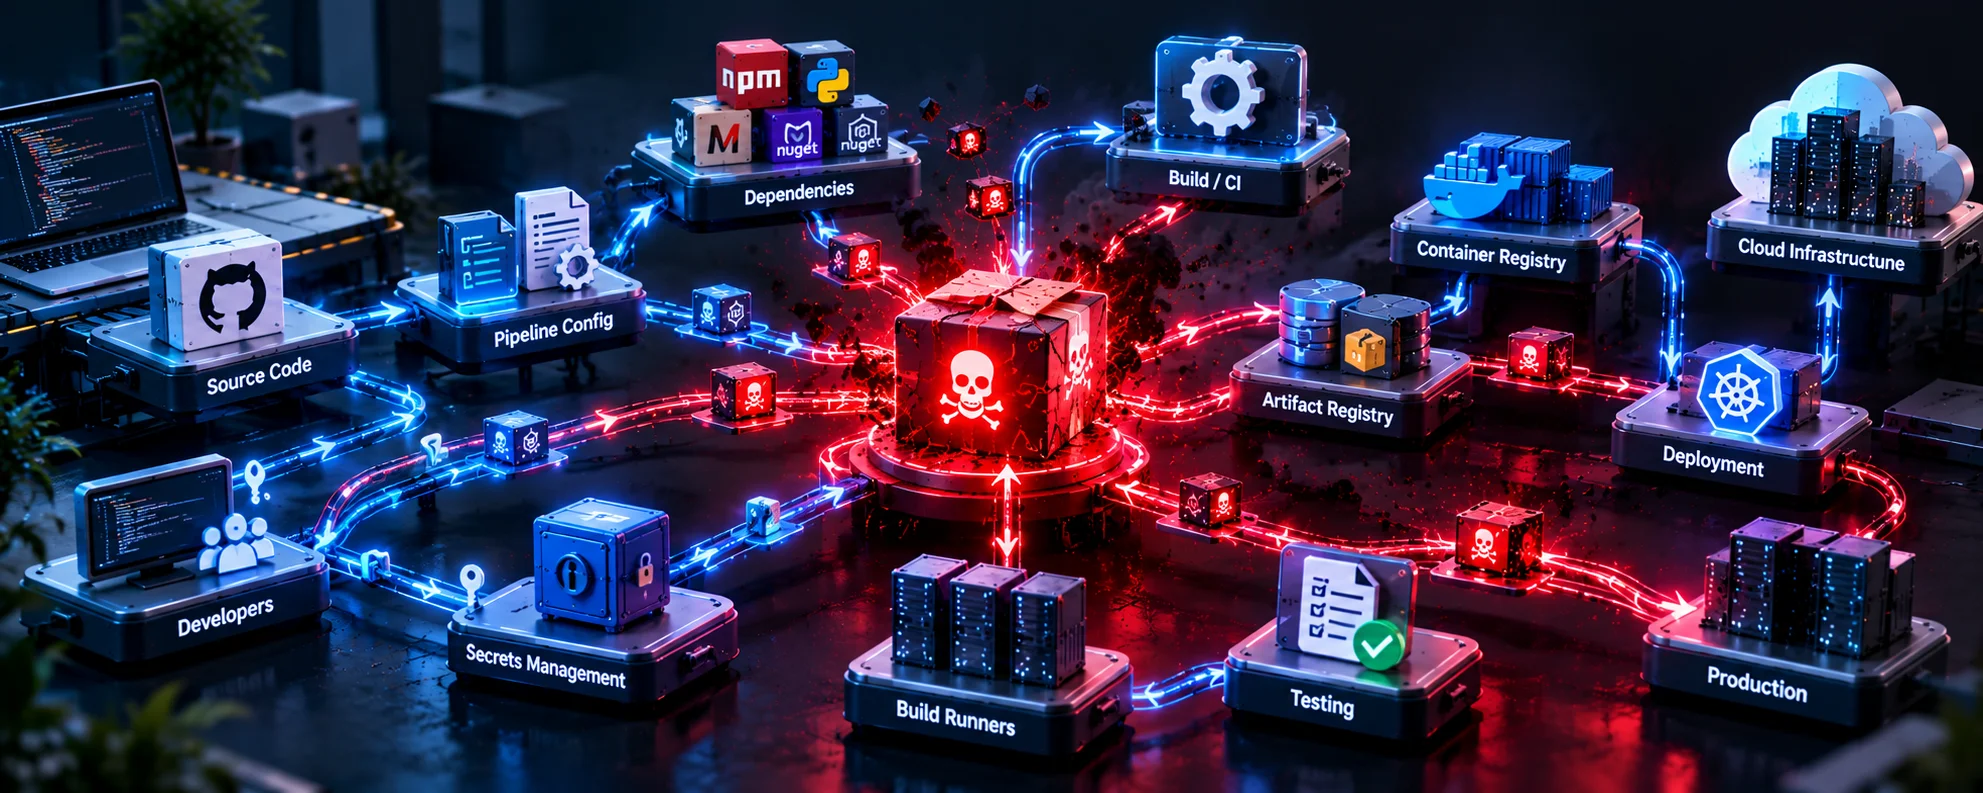
The Security Risks Hidden Inside Your CI/CD Pipeline

Continuous integration and continuous delivery (CI/CD) pipelines automate how software is built, tested, and deployed. They help development teams release changes faster, but they also connect source…

· 3 min read
Third-Party & Supply Chain Risk

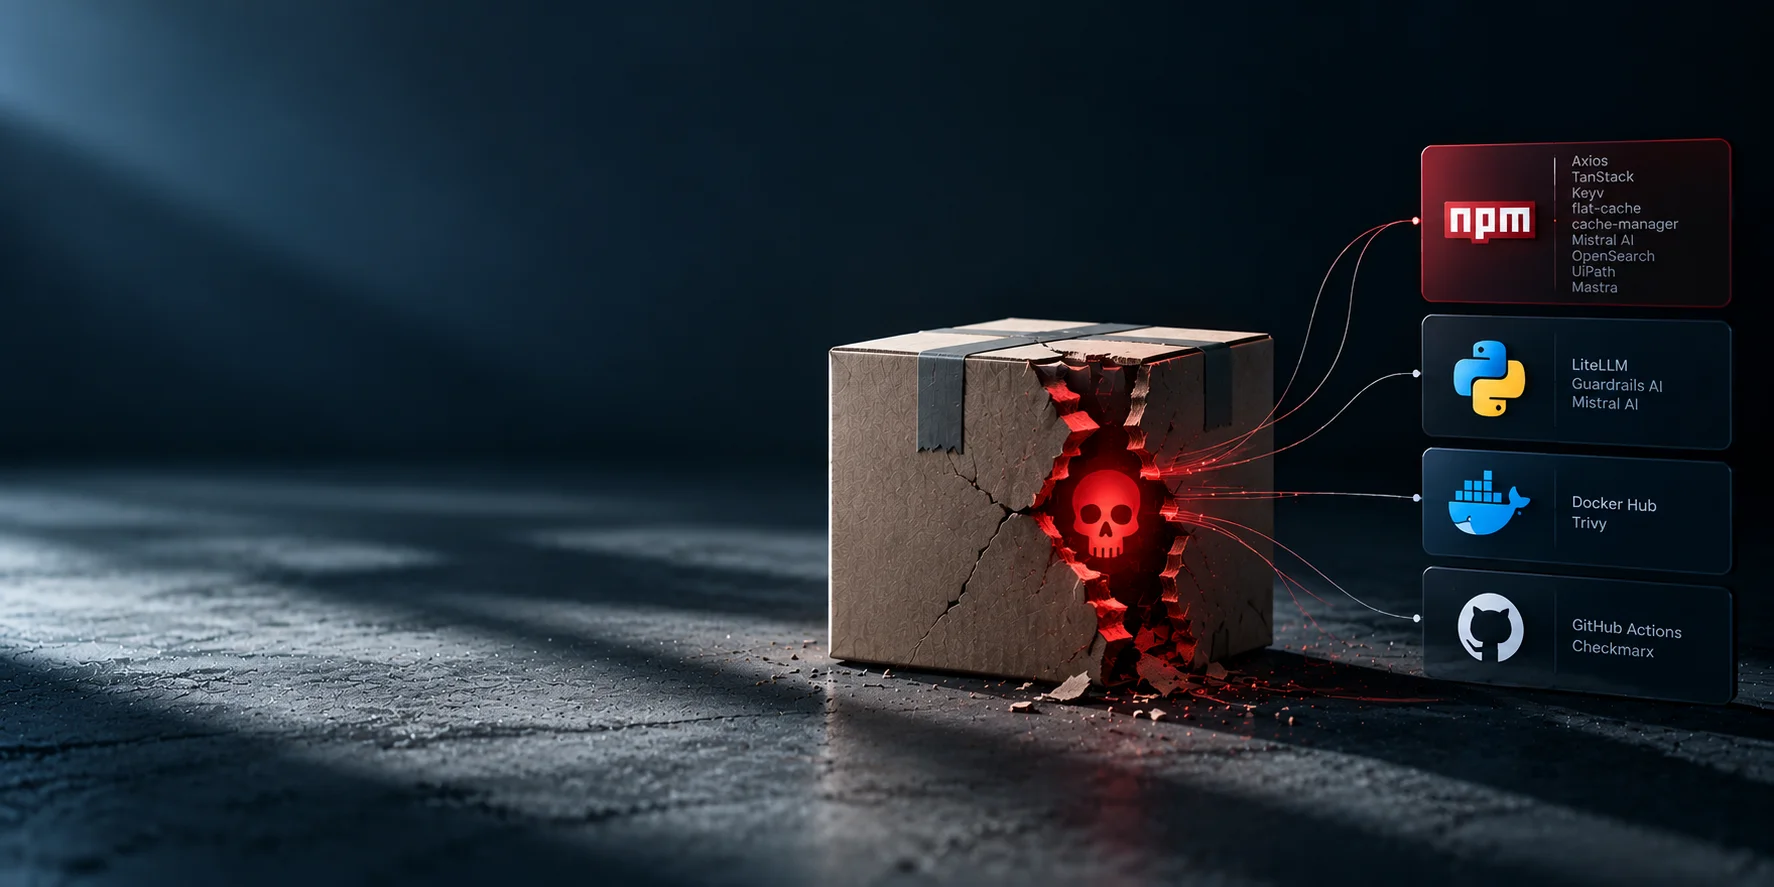
When Trusted Software Becomes the Attack Vector

organizations rely on trusted software vendors, signed updates, and established distribution channels to maintain their systems. However, trust in a software provider does not guarantee that every update or component is secure. If attackers compromise a vendor's development environment or distribution infrastructure, legitimate software can become a delivery mechanism for malicious code.

· 4 min read
Third-Party & Supply Chain Risk

Software Supply Chain Attacks Are Hiding in Your Dependencies

Software supply chain attacks exploit vulnerabilities in third-party dependencies, compromised packages, and CI/CD pipelines. Learn how these threats affect modern applications and the security measures organizations can implement to protect software integrity.

· 3 min read