Responding to a Software Supply Chain Compromise
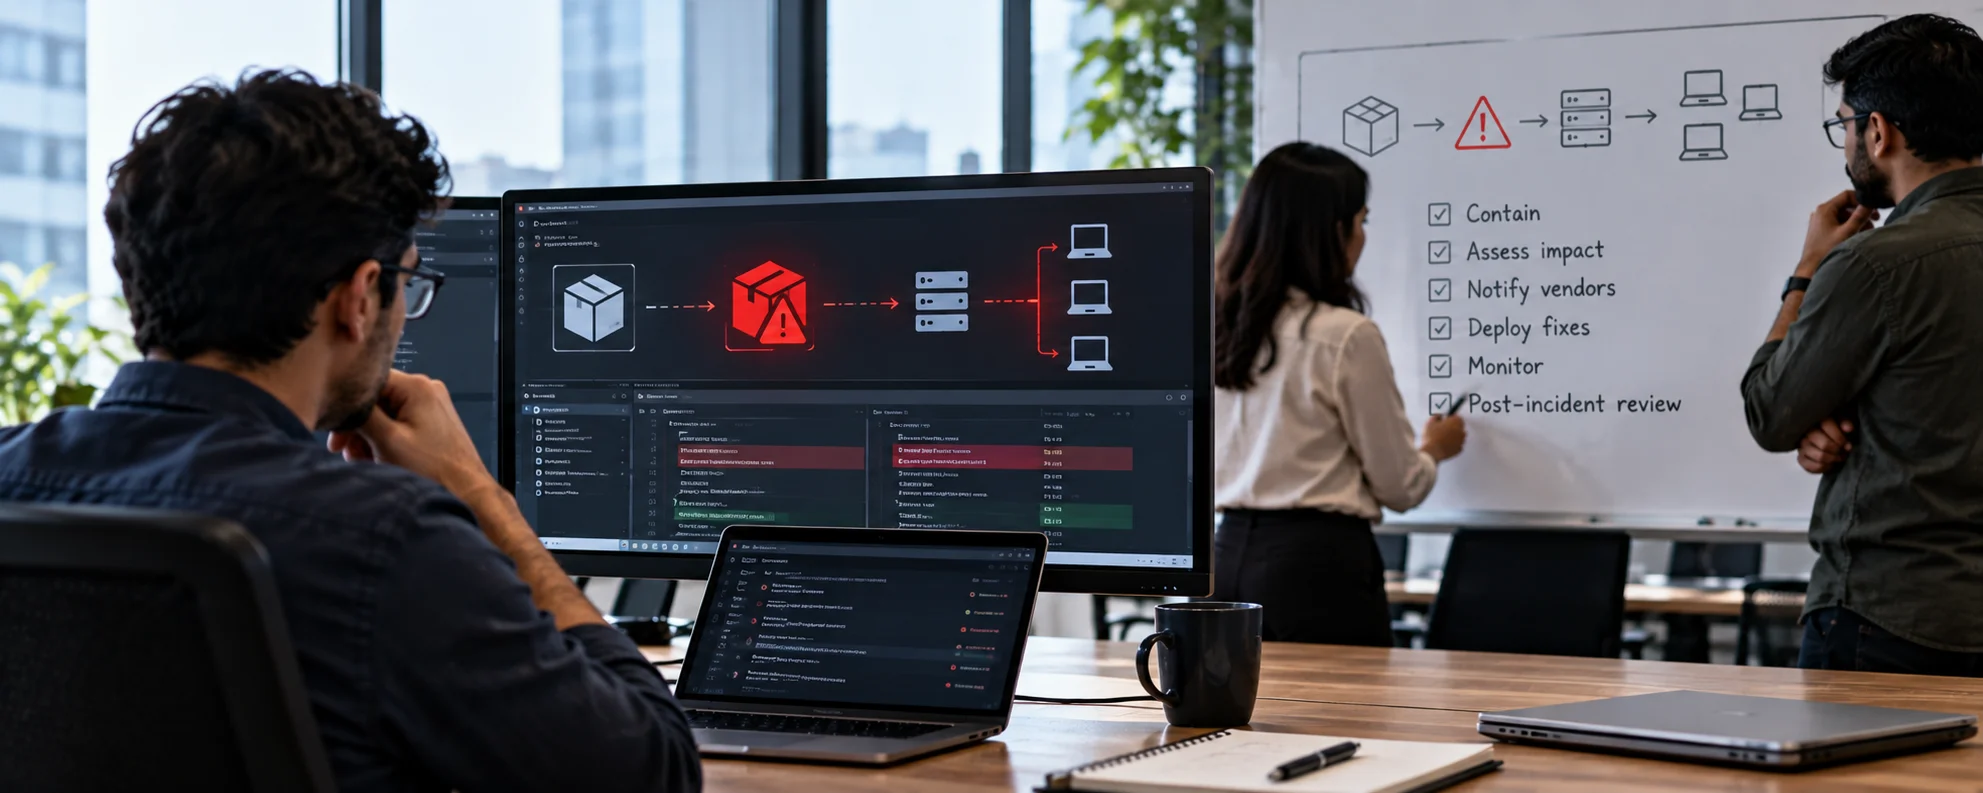
A software supply chain compromise can affect multiple applications, development environments, and production systems simultaneously. Identifying the affected component is only the first step.…
Research, field notes and practical guidance from the people who break into systems for a living, so you can defend yours.
A software supply chain compromise can affect multiple applications, development environments, and production systems simultaneously. Identifying the affected component is only the first step.…
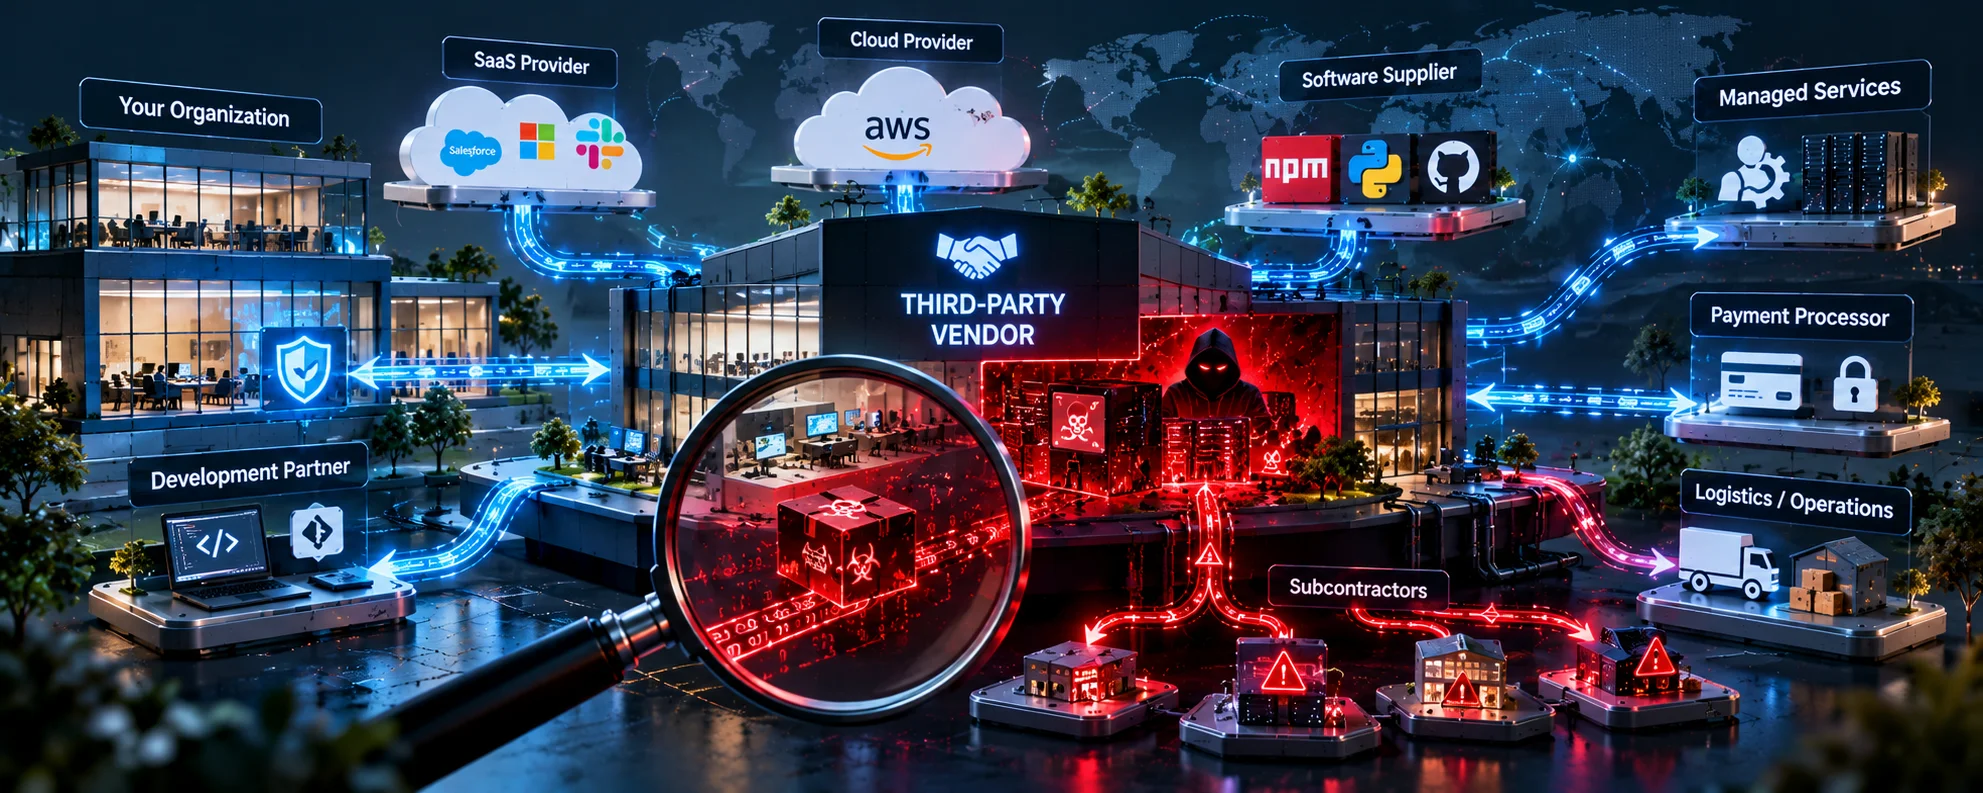
A vendor can pass a security questionnaire, provide industry-recognized certifications, and demonstrate documented security policies while still introducing significant risk into an organization's…
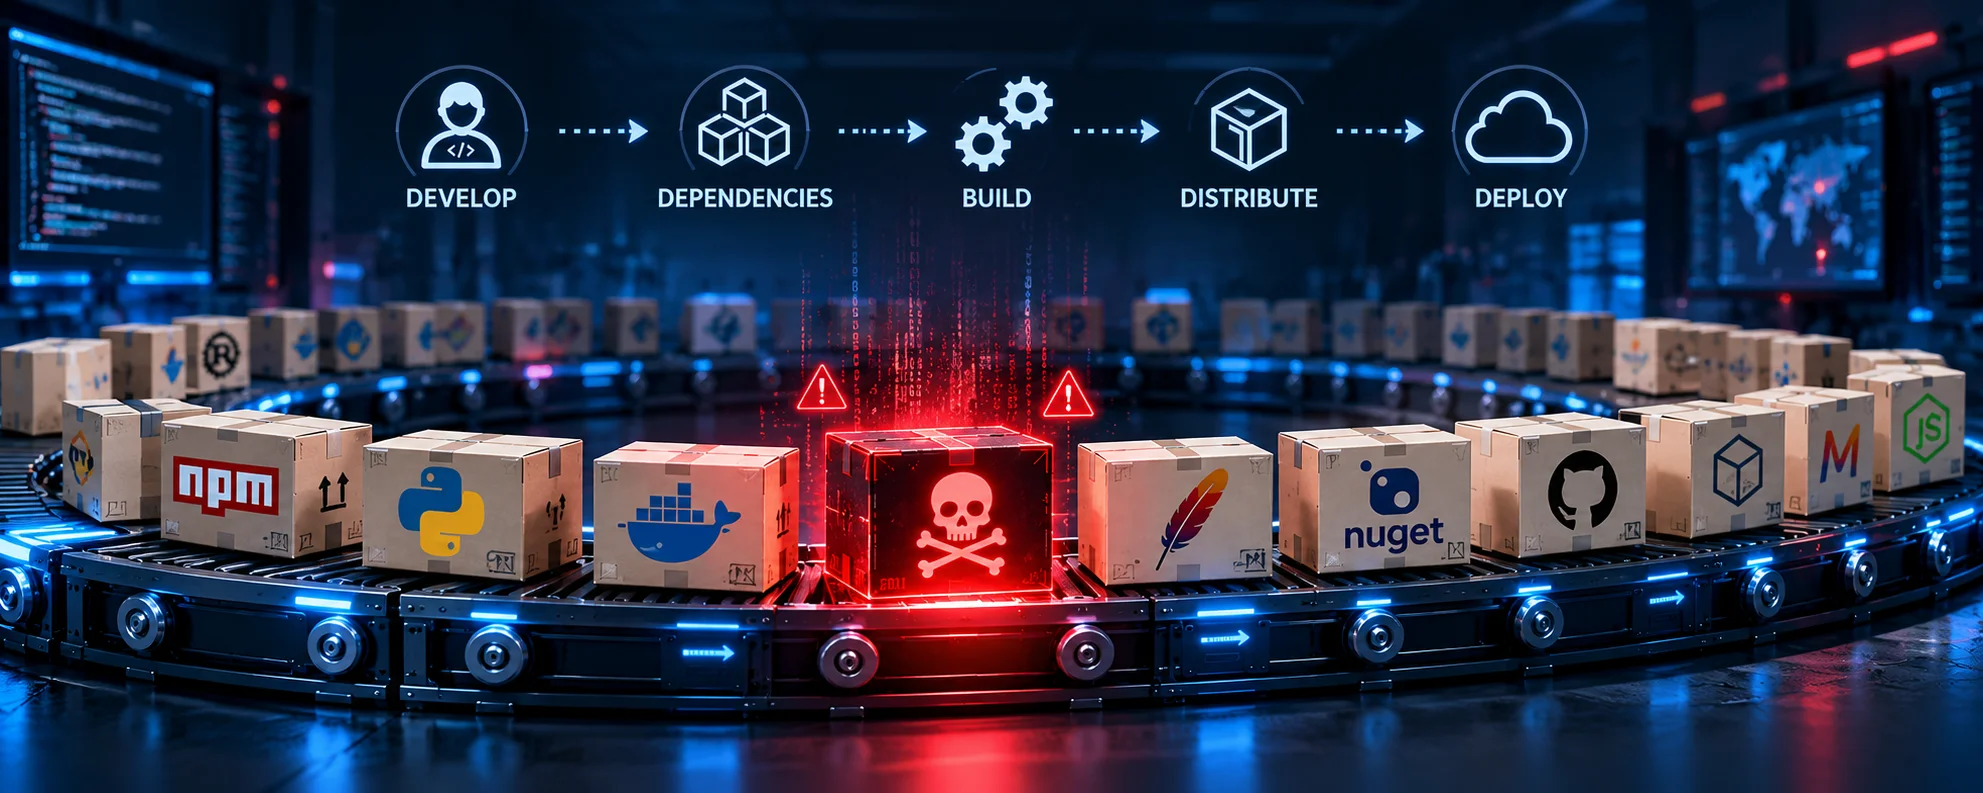
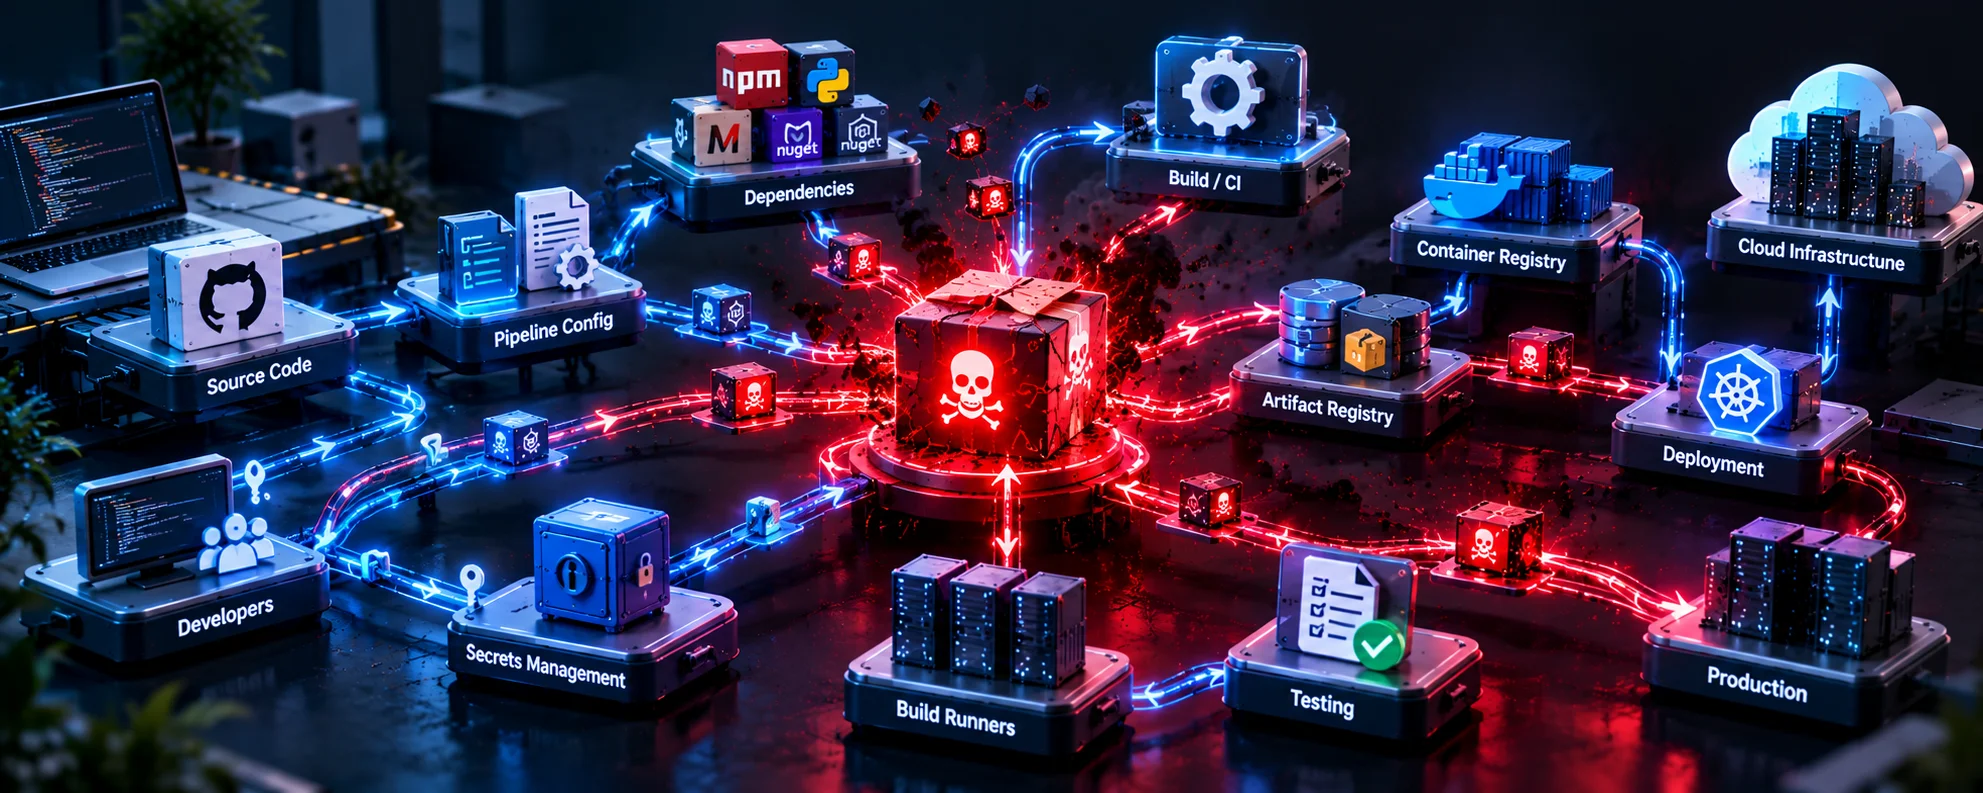
Continuous integration and continuous delivery (CI/CD) pipelines automate how software is built, tested, and deployed. They help development teams release changes faster, but they also connect source…
organizations rely on trusted software vendors, signed updates, and established distribution channels to maintain their systems. However, trust in a software provider does not guarantee that every update or component is secure. If attackers compromise a vendor's development environment or distribution infrastructure, legitimate software can become a delivery mechanism for malicious code.
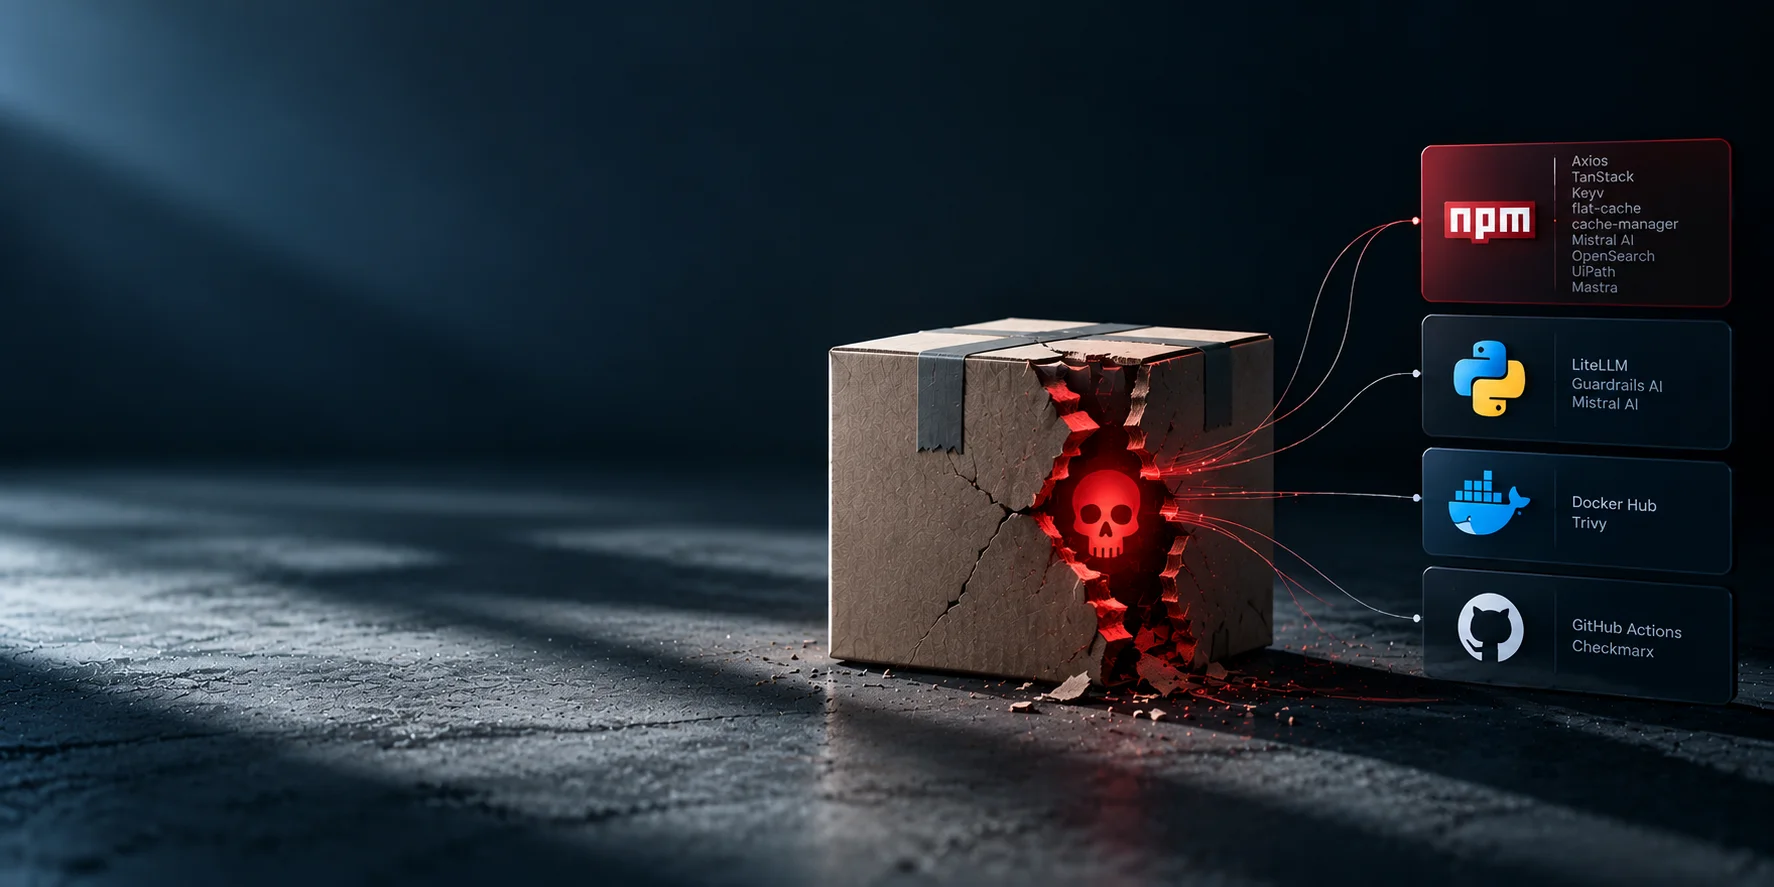
Software supply chain attacks exploit vulnerabilities in third-party dependencies, compromised packages, and CI/CD pipelines. Learn how these threats affect modern applications and the security measures organizations can implement to protect software integrity.